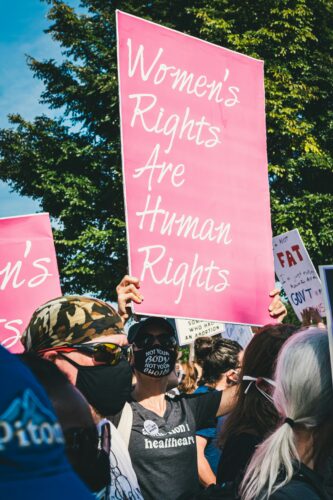
It’s been a little over three years since the Supreme Court’s unprecedented overturning of Roe v. Wade, and since then states have continued down two opposing paths that either restrict or protect access to reproductive health care. Over the past year we have seen an uptick in legal actions as courts have become more involved, particularly in addressing conflicts between state laws. We also continue to see digital data used to track people seeking and providing reproductive health care. That marks an escalation in efforts to gain access to more information about individuals’ health choices and to use that to punish those people for seeking or providing reproductive health care.
Increasingly, states hostile to reproductive care are turning to courts, in particular to enforce their laws against abortion providers in other states. Texas and Louisiana have sued out-of-state doctors who prescribe abortion medications to their residents. These legal actions have faced strong opposition from other states like New York which have enacted laws to shield and protect providers and recipients of reproductive health services from investigations. This conflict is likely to continue and to take on new dimensions as states hostile to reproductive health care seek records from states with shield laws. It is currently unclear how these conflicts of laws will be resolved.
States and other aggrieved parties have also challenged federal reproductive privacy protections. In the spring of 2024, the Department of Health and Human Services’ (HHS) Office of Civil Rights (OCR) announced an update to the Health Information Portability and Accountability Act (HIPAA) Privacy Rule to support reproductive health care privacy (2024 Rule) (which CDT supported upon its initial release). The rule, as updated in 2024, prohibits health care entities like doctors and insurance companies from complying with requests from law enforcement involving reproductive health care for use in an investigation or prosecution if the care was legal in the state where the care was provided. The rule was designed to increase the trust between patients and doctors, as patients who fear their medical data might be shared without their knowledge, and even used against them in court, might otherwise be deterred from seeking care.
Many states challenged the 2024 rule, including Texas and Tennessee (which was joined by 14 other states). Texas’ action challenges not just the 2024 Rule, but also the entire HIPAA Privacy Rule, in existence since 2000. In another case, Purl v. Department of Health and Human Services, a doctor in Texas sued the federal government because she claims the updates to the privacy rule could prevent her from reporting possible abuse. The district court judge recently sided with the doctor and vacated the 2024 rule nationwide.
If the lower court’s decision withstands any appeal, it will diminish health care outcomes. If patients can’t trust that doctors and insurance companies will keep their reproductive health data private, patients are less likely to be candid and open with their doctors or to seek care in the first place.
In this environment, companies that collect and share data must be good stewards of that data and be cognizant of the myriad ways that the information they collect can reveal people’s health status, including those seeking and accessing legal reproductive health care. Many types of data can reveal sensitive information about a person’s health and healthcare choices. Search queries, browsing history, the contents of electronic communications, and a person’s location data can all reveal such private information, despite not typically being thought of as sources of “medical” or health-related data.
As a result, companies inside and outside the healthcare sector must follow best practices and carefully assess and limit the private information they collect, store, and share. Without thoughtful action, a company’s data practices may be complicit in exposing its customers to criminal prosecution or to civil litigation for health care that is still legal in the majority of the United States and that was constitutionally protected for almost 50 years.
CDT and Partners Urge Passage of the California Location Privacy Act of 2025 (AB 322)
Location data is particularly sensitive, and when collected across time it can reveal a broad range of intrusive insights such as medical conditions, sexual orientation, political activities, and religious beliefs.
CDT and Allies Urge FCC Not to Violate Privacy of Cell Phone Buyers
CDT and EPIC led a coalition of 15 organizations in urging the FCC not to require phone companies to collect government IDs, physical addresses, and alternate phone numbers from every phone subscriber in the country.
As Brussels starts emptying for the summer, the risks of frontier AI models continue to capture the attention of policymakers as a key chapter of the AI Act becomes enforceable, and disclosure rules around the use of AI systems and AI-generated content are further clarified.